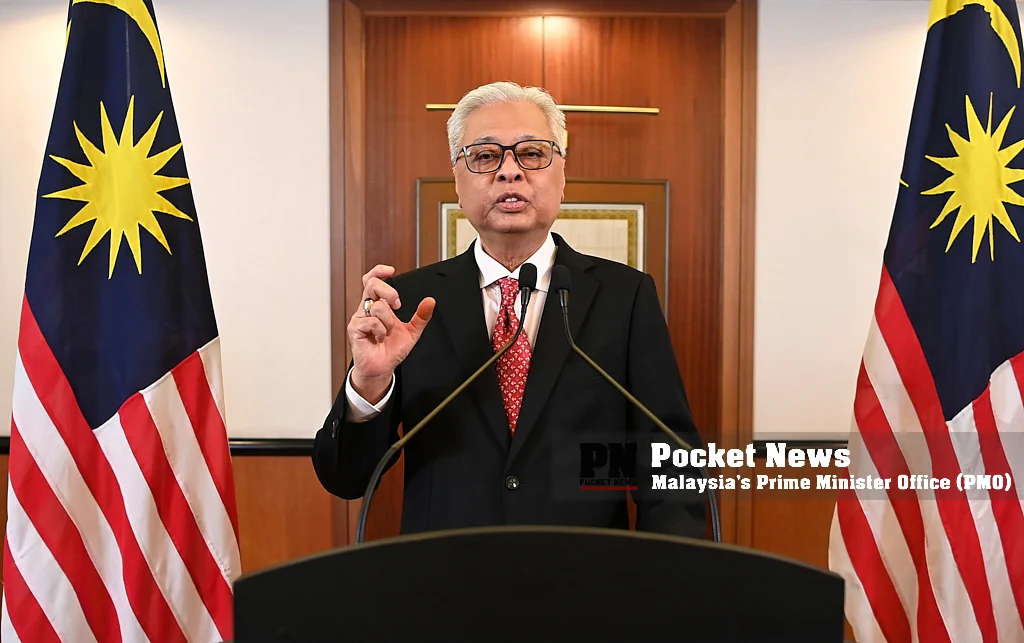

KUALA LUMPUR, January 4 — The Pangkalan Data Utama (Padu) marked its official launch with a grand event in Putrajaya, but within hours of its public debut, critical flaws emerged in the government’s flagship digital project. The most prominent issue involved MyKad, highlighted by former Deputy Minister of International Trade and Industry, Ong Kian Ming. However, a more severe concern was discovered in the centralized database, as developer and user @drmsr_dev revealed that Padu account passwords could be easily changed using an individual’s IC number.
In a set of screenshots shared on social media, drmsr_dev demonstrated how this flaw could be exploited through API calls. Following public exposure, the Padu team swiftly changed the API to address the flaw, as confirmed by drmsr_dev in a subsequent tweet. The Ministry of Economy acknowledged the security issue, noting ongoing improvements and describing the discovery and subsequent feedback as “positive criticism.”
Given Padu’s handling of personal data for millions of Malaysians, security concerns were already prevalent. This critical flaw further raises doubts about the public’s confidence in the centralized database’s ability to safeguard data. Considering recent data leaks involving government agencies, including Socso, JPN, and MCMC, Padu’s effectiveness in achieving its objectives may be hindered if public trust is compromised. Questions regarding the extent of Padu’s testing and security audits before its launch have started to emerge, even though credit is given to the administrator for prompt fixes.